Connect with us

Tech

IoT Is A Beast With Double-Edge Sword

Published

on

The Internet of Things, also referred to as the Internet of Everything, is the science and art combined to turn everyday dormant objects and devices that operate in isolation today into “live” beasts, communicating with each other, feeding on data, and using the internet as the skeleton backbone that enables communication and interaction to brings these inactive objects into the era of smart internet connectivity.

Internet of Things (IoT) is considered to be a technology tsunami that will dwarf the internet wave by miles. It is already taking over our way of working, studying, playing and living by storm. And just as we have witnessed billions of dollars vanish into thin air due to cybersecurity vulnerabilities, IoT devices, personal data and privacy are heading to face the same challenges. In fact, IoT is destined to be exposed to even greater risks since 99% of devices that are not connected at present, one by one begin to make their way into the connected future we will live in.

While that sounds like from a futuristic Hollywood movie, Star War like, the IoT phase has already began as early as 2010 with the rise of smartphones. And just as it will bring all those beautiful advancements, it also carries tremendous dangers and great concern within its folds.

The latest report to highlight these risks and challenges comes from The National Institute of Standards and Technology (NIST), a US based organisation that is part of the U.S. Department of Commerce. The 34 page report titled “Considerations for Managing Internet of Things (IoT) Cybersecurity and Privacy Risks” can be downloaded here for full details.

With the rapid rise of IoT, the report highlights that since there are a lot of organizations that are not fully aware of their use of IoT, consideration of cybersecurity and privacy risks in turn might not have been fully understood or appreciated. The report shines the spotlight on three major considerations that every organization out there needs to identify, treat and govern. These considerations are summarized as below:

  1. IoT devices often do not interact with the physical world in the same ways conventional IT devices do.
  2. IoT devices often have various ways to be accessed and managed that are not typical to the ways traditional IT devices operate.
  3. As IoT devices are being created by thousands of companies without proper standards, the current effectiveness of cybersecurity and privacy controls of established devices do not apply to IoT which poses tremendous concerns.

The report further expands and offers some high level “risk mitigation goals” by raising awareness that IoT devices need to have security protection that extends to the Device, Data and Individual privacy.

“Organizations should ensure they are addressing the cybersecurity and privacy risk considerations and challenges throughout the IoT device lifecycle for the appropriate risk mitigation goals and areas.” The report highlights.

NIST being a non-regulatory organization, it was aiming mainly to bring forth awareness and guidance. There are currently no internationally accepted standards for IoT, and while there is a “reference framework for IoT” released by the International Organization for Standardization (ISO), by a standard referred to as ISO/IEC 30141, unfortunately most new players and producers of IoT devices are not following these standards. Enforcing the right practice is still in its infancy and have not taken hold, which poses challenges possibly beyond our current understanding.

For now, it is up to organizations and consumers to carefully handle this double-edge sword, and a guide such as the one published by NIST should not be taken lightly.

Continue Reading
Click to comment

Leave a Reply

Your email address will not be published. Required fields are marked *

Business

IoT Risks – What Are You Doing About It?

Published

on

The Internet of Things (IoT) and Industrial IoT (IIoT) have started to see some genuine energy, specifically in industries such as medical care, manufacturing and the retail sector. More and more gadgets, devices, vehicles and buildings, as well as various other objects are being geared up with sensing units and connected, allowing the sharing of data that provides valuable in-depth analysis for businesses using it.

As one might expect, the issue of security has constantly been an interest in IoT, which has not vanished as more organizations introduce tasks. In fact, security problems are most likely to come to be even more intricate as companies work with companions throughout their supply chains in initiatives to produce “smarter” atmospheres and also a lot more efficient procedures.

The IoT main security issues is fuelled by the high expansion in linked devices, the lack of a central IoT risk management program, as well as the absence of senior-most authority’s involvement.

The soaring number of IoT gadgets that can give access to sensitive business data conspire to make IoT risk management an extremely convoluted undertaking. In addition, the availability of a raising number of IoT devices to exacerbate dispersed denial of service strikes includes even better urgency to the risk mitigation timeline. Even the high-performing organizations require to improve many elements of their IoT danger management capacities.

Quick improvements are needed throughout a lot of IoT run the risk of monitoring programs and third-party threat administration (TPRM) in general. The locations where enhancements are required consist of governance, danger as well as asset management practices, and resource allowance.

Study participants expect the variety of IoT devices they count on to efficiently double with the next 2 to 3 years. A lot of the respondents indicated that unprotected IoT tools are significantly likely to have materially disruptive repercussions; yet virtually 60% also acknowledge they do not know whether third-party controls are adequate.

With the majority of the organizations reporting a lack of understanding and also adequate devices to determine which IoT tools have appropriate safety, the number of real violations and also cyber attacks linked to IoT gadgets is most likely significantly higher than the variety of occasions reported.

The team of self-proclaimed greater entertainers rate their ability to handle IoT and also other third-party risk as “very efficient.” This shows that IoT health practices in the vast majority of organizations require substantial improvement, the research said.

Organizations need to bridge the gap in between understanding and as well as practice. Current IoT threat administration is identified by insufficient threat management structures, resources, interest, as well as mitigation strategies.

They need to develop a stronger threat culture. Individuals throughout the IoT environment need to better comprehend the threats posed by the technology, as well as organizations have to guarantee that IoT safety is taken seriously by management whatsoever degrees.

They additionally need a lot more IoT threat management responsibility. A mature IoT danger management framework is important to ensuring that the protection of the IoT modern technologies meets defined danger resistances.

Lastly, organizations require much more reliable IoT control validation paradigm structured on a “depend on, yet verify” design. Today, firms rely upon third-party agreements and plan reviews, placing focus on the trust aspect of IoT controls without sufficient confirmation.

Continue Reading

Politics

Political Targeted Advertisement Will Have No Place On Google

Published

on

Google has announced on Wednesday through a blog post that an update to the “political ads” policy will be rolled out in the aim to limit political campaigners to be targeted based on user’s political association on Google search, email addresses or interests. With that said, other demographic information such as gender and location may still be used too target audiences.

The company is also hoping to restrict intentionally misleading information and doctored media which is known as “deepfakes” in ads, on its platforms Google search and YouTube and also includes display ads that appear on other websites.

Google explains in the announcement that “given recent concerns and debates about political advertising, and the importance of shared trust in the democratic process, we want to improve voters’ confidence in the political ads they may see on our ad platforms. So we’re making a few changes to how we handle political ads on our platforms globally.”

For the UK the policy will be enforced within a week, in preparation for the UK country election due on 12 December. Other countries will follow suit, whereby the policy will roll out to the EU by end of the calendar year, and be enforced worldwide by 6th of January 2020.

The move comes as a response to criticism that Google and Facebook received after showing ads with misleading information that accused former Vice President Joe Biden of corruption, as well as earlier interference of Russia into the 2016 US elections.

Continue Reading

Politics

Uber Back-Up Driver Watched “The Voice” As She Runs Over Victim

Published

on

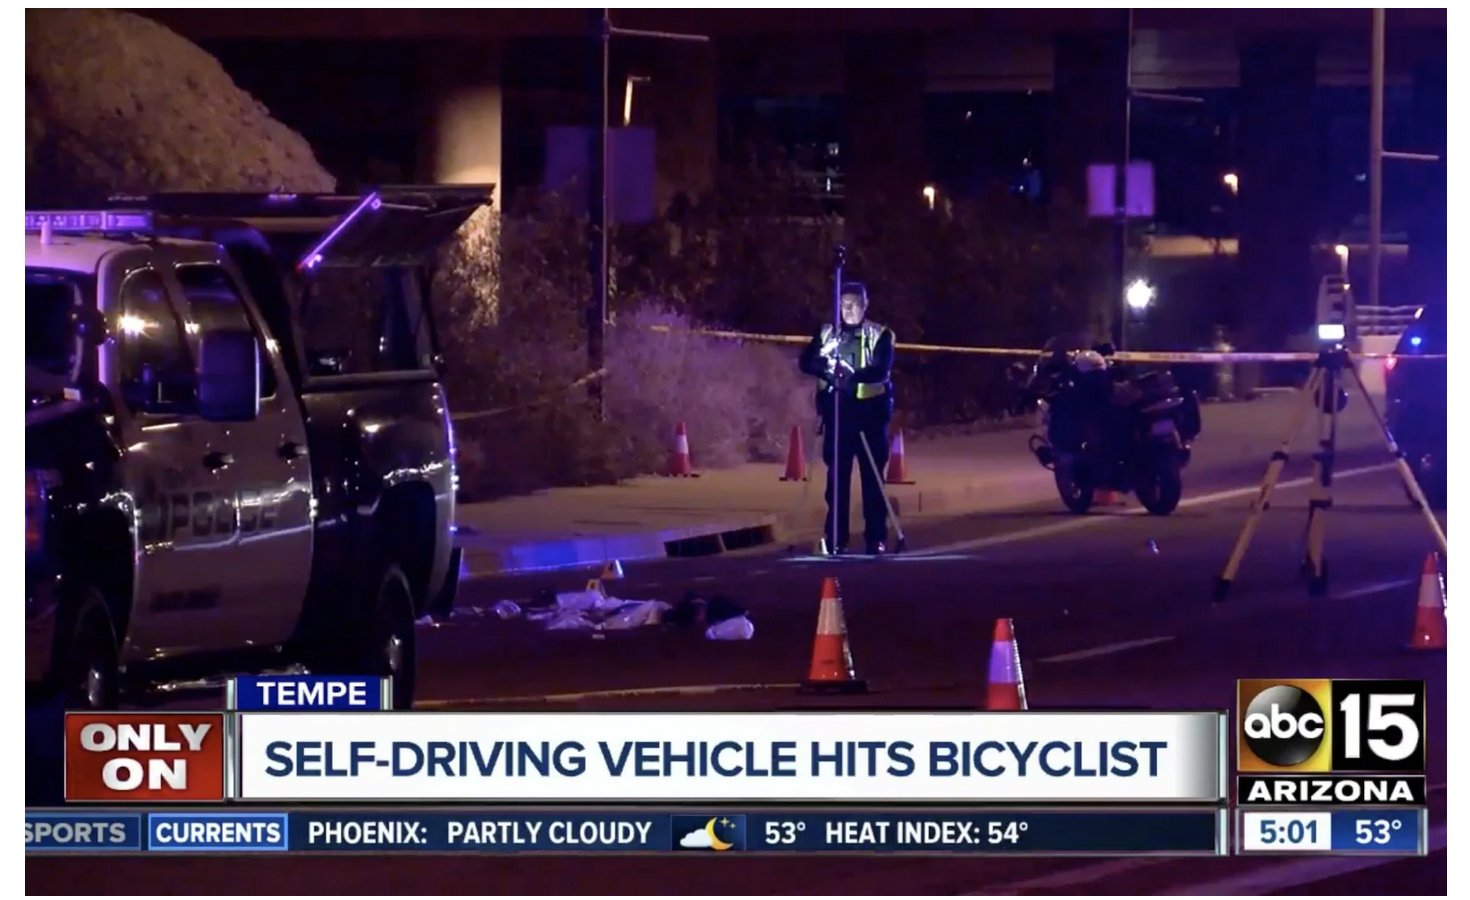
A final report by The National Transportation Safety Board (NTSB) has been released on the investigation of the fatal accident that took the life of Elaine Herzberg, 49 years old, who was killed while crossing the road on the 18th March 2018.

The distracted driver, Rafaela Vasquez, 44 years old, who was behind the wheel of an Uber car, the report suggests, was to blame as the primary cause of the accident as she was streaming “The Voice” on her smartphone instead of paying attention to the road. She was taking her eyes off the road at 34% of the time, with the last 6 seconds before impact Vasquez was looking down at the TV show. She is still in custody and may be charged for manslaughter.

The report also blamed the safety culture at Uber, noting that lack of proper monitoring of back-up drivers by the company has led to carelessness of its drivers. The car was intended to be performing tests into driverless technologies and automation, it was not fully autonomous or ready to be on the road without fully attentive driver behind its wheel.

NTSB also noted that the third component that led to the accident, was the victim herself, of which toxicology tests confirmed she was high on methamphetamine, and therefore was not paying much attention to the road, walking in the path of the incoming car and not using an official pedestrian crossing.  

Lack of proper regulation at State and Federal levels was also mentioned in the report as factor that led to negligence of companies such as Uber on enforcing better standards while testing autonomous cars.

Continue Reading

Trending